Enterprise Data Leak Monitoring
that turns exposure into action.
LeakWatch by RedSide is a dedicated Data Leak Monitoring platform for organisations of all sizes. We continuously scan vetted breach and leak sources for your corporate and partner identities, helping you prevent account takeover, credential‑stuffing and brand abuse.
- Full visibility into exposed usernames, emails and domains across curated leak datasets.
- Risk‑based prioritisation so your SOC focuses on the incidents that matter most.
- Operational workflows that plug directly into your SIEM, SOAR and ticketing tools.
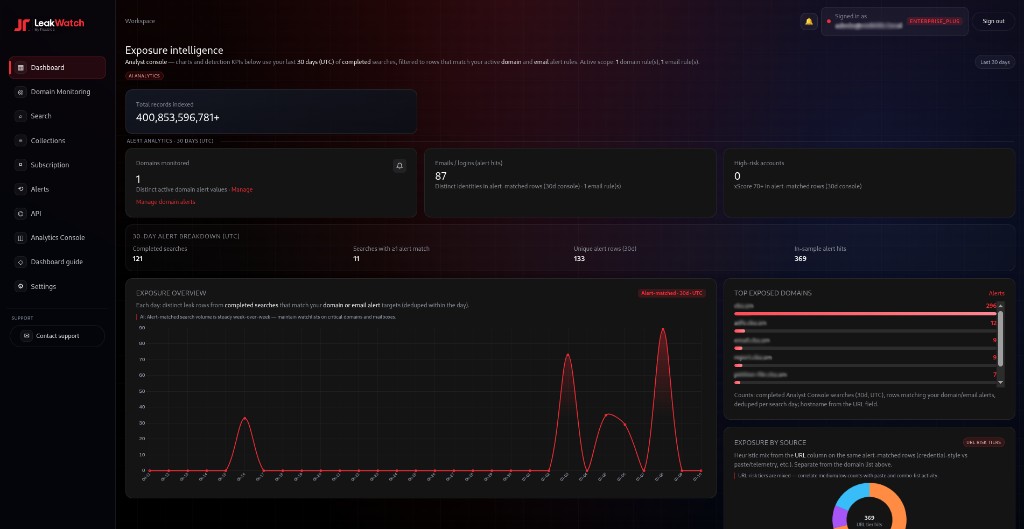
Your exposure intelligence dashboard after sign-up
Enterprise and Enterprise Plus workspaces get a live Exposure intelligence view: 30-day alert analytics, trend charts, domain and URL risk breakdowns, and recent matched leak rows — scoped to your active domain and email alert rules.
Detect exposed credentials fast
Continuously monitor curated breach and dark‑web sources for credentials tied to your domains, brands and high‑risk user populations.
- Search across millions of leaked records in minutes.
- Identify compromised corporate, privileged and VIP accounts.
- Spot reused passwords and shared credentials.
Prioritise what matters
Move from raw data to clear, risk‑ranked incidents your analysts can act on immediately.
- Scoring tuned for role, sensitivity and reuse patterns.
- Contextual metadata to inform response decisions.
- Filters for business units, geographies and partner domains.
Orchestrate response
Embed credential leak intelligence into your existing playbooks so remediation is consistent and auditable.
- Email and webhook alerts for high‑risk accounts.
- SIEM and SOAR integrations for automated workflows.
- Exportable reports for incident and board‑level updates.
How LeakWatch supports your security programme
- Reduce account‑takeover risk by identifying exposed credentials before attackers can weaponise them.
- Strengthen identity security by aligning leak intelligence with MFA, password‑reset and zero‑trust initiatives.
- Support compliance frameworks such as SOC 2, ISO 27001 and GDPR with demonstrable continuous monitoring.
- Enhance incident response with faster scoping of compromised accounts and structured evidence for investigations.
- Extend visibility to third parties by monitoring supplier and partner domains where appropriate and lawful.
Security, privacy & responsible use
LeakWatch is engineered for authorised defensive security operations only. We do not perform credential stuffing, password cracking or any intrusive testing on your behalf.
Access to intelligence sources is tightly controlled, credentials are never stored in cleartext, and all activity is captured in audit logs for compliance and incident‑response workflows.
For details on how we handle data, please refer to our Privacy Policy and Terms of Service.
Ready to assess your credential exposure?
Schedule a guided demonstration with our team to see how LeakWatch discovers exposed credentials for your organisation and how quickly you can move from insight to remediation.